Manufacturing & OT
Find reachable PLC, SCADA and fieldbus services such as Modbus, S7comm, EtherNet/IP and PROFINET before an attacker does.
- ICS/SCADA
- Segmentation checks
Self-hosted security operations
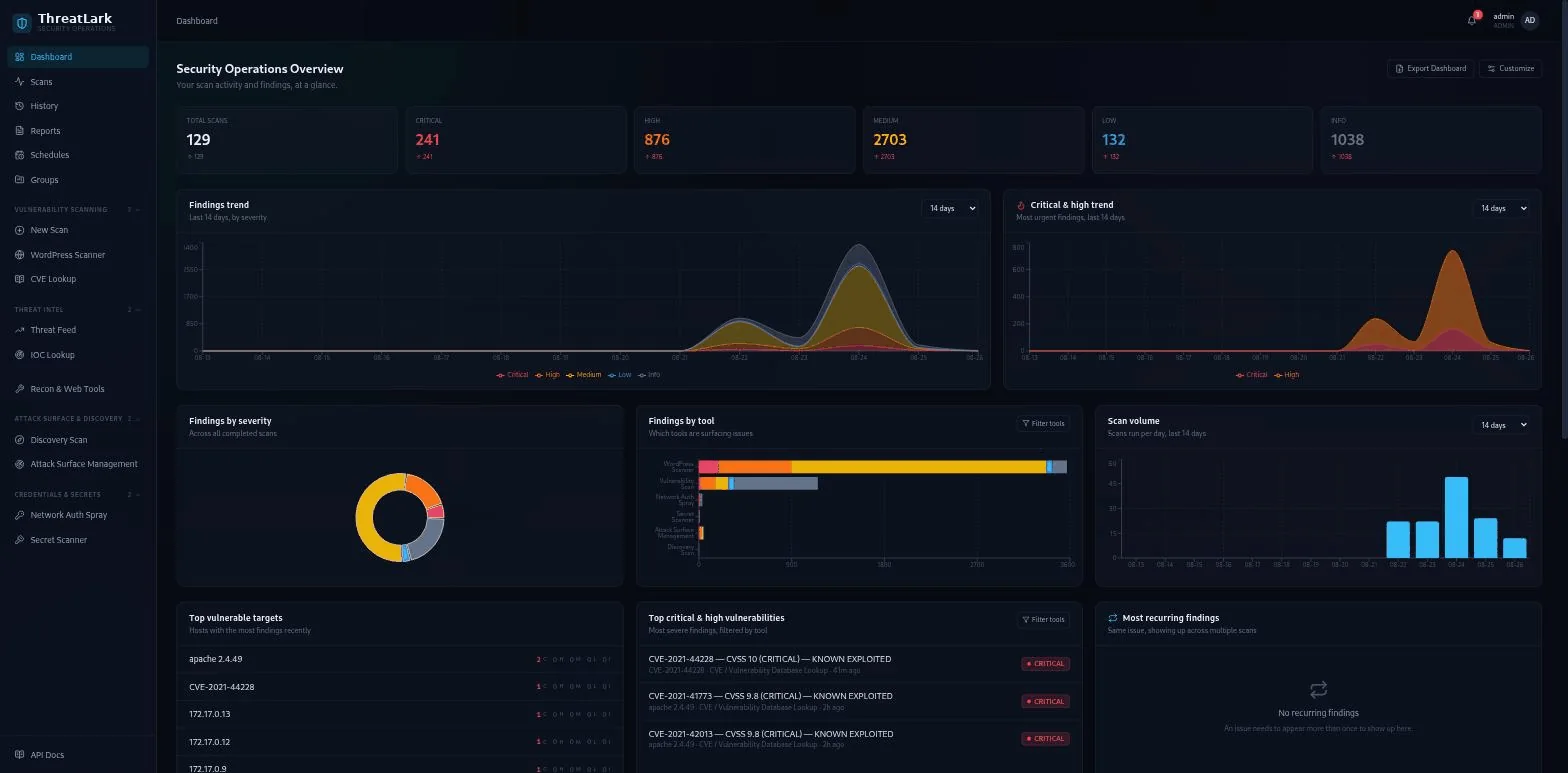
Comprehensive discovery scanning of massive CIDR ranges, attack surface management, OT/IoT and vulnerability scanning, self-hosted in your own perimeter.
Runs inside your networkRead-only OT probingSARIF 2.1.0 export
Sweep huge CIDR ranges into named groups of live hosts.
130+ exposure checks, 64 OT/IoT protocols and a plugin-driven vulnerability scanner.
A fix-first score weighing severity, CISA KEV, EPSS and asset criticality.
HTML, PDF, CSV and JSON exports, plus SARIF 2.1.0 for your pipeline.
From the first sweep of an address range to a report your engineers can act on. Discovery, assessment and prioritization share one set of assets, groups and findings.
Fast live-host sweeps built on nmap host discovery, designed for large internal address space.
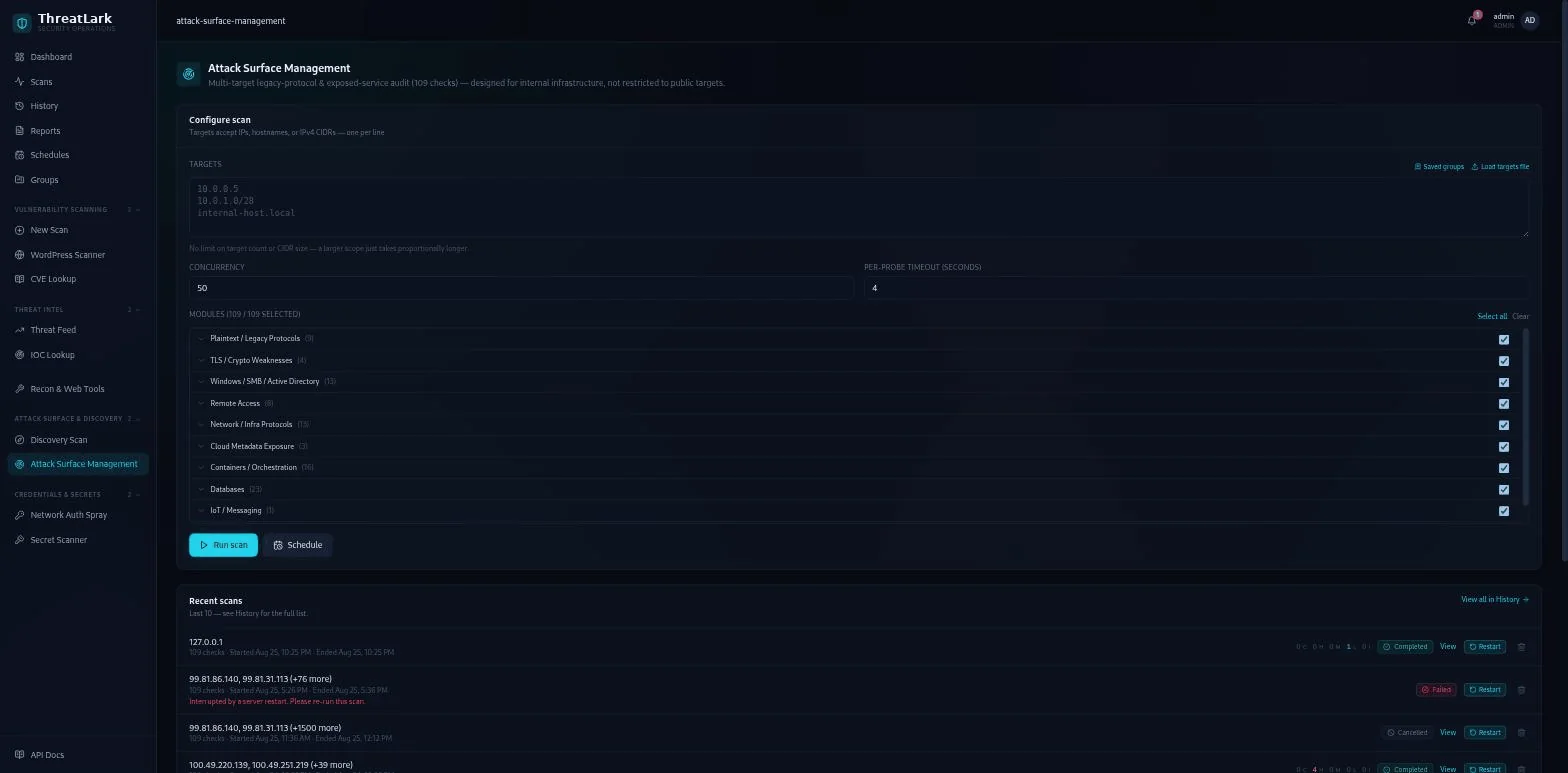
A read-only audit of 130+ legacy-protocol and exposed-service checks, built for internal infrastructure as well as the perimeter.
A dedicated OT/IoT Exposure scanner covering 64 industrial, building-automation, energy and IoT protocols.
The New Scan engine combines core web checks with an optional chain of 20+ best-in-class open-source scanners.
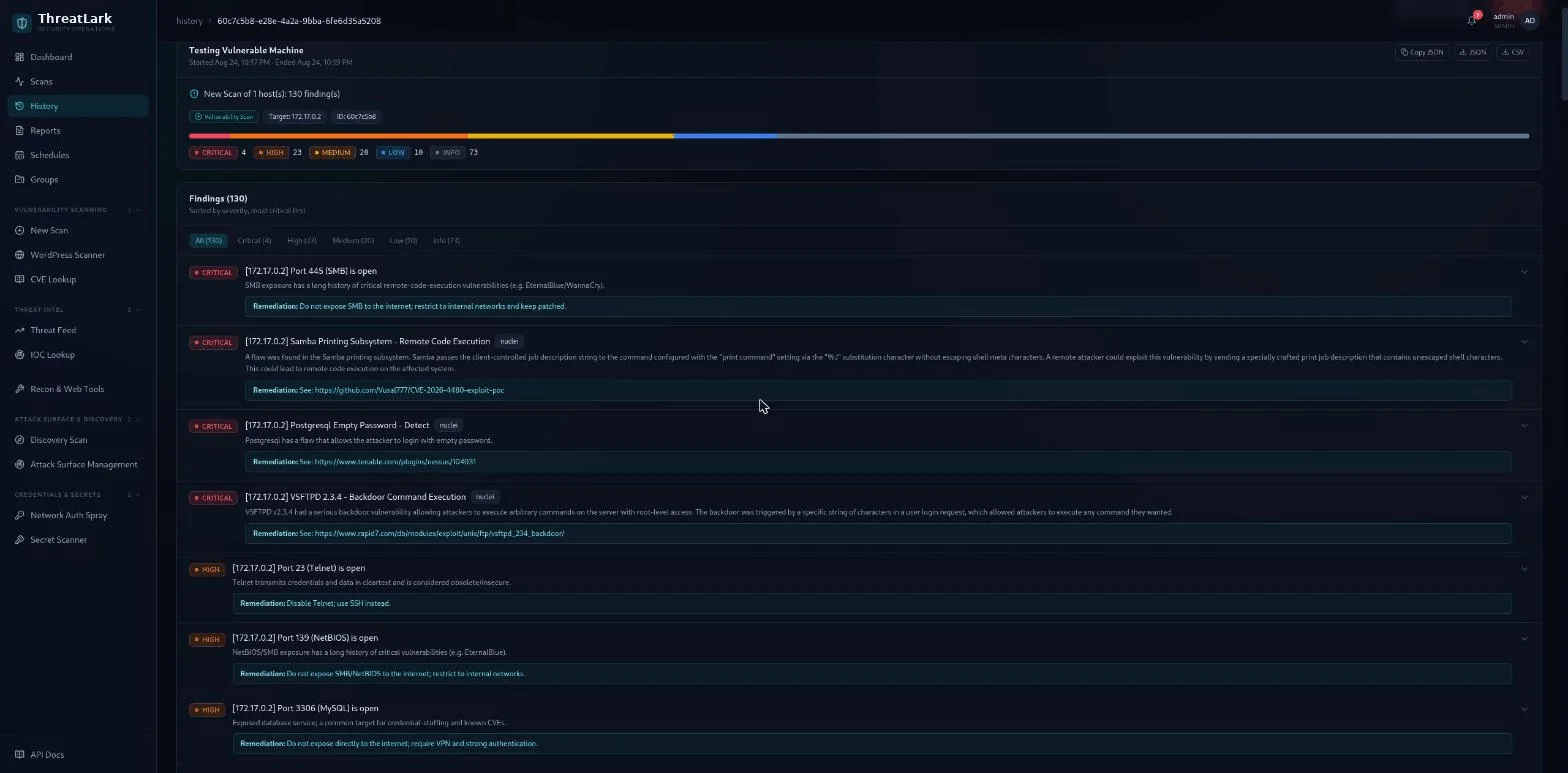
De-duplicated findings, a documented priority score and exports that fit the way your team already works.
Fix-first priority score (0-100)
Export formats
Also included: WordPress Scanner, API Security Scanner, Container Scanner, Network Auth Spray, Secret Scanner, CVE and IOC lookup, ThreatPulse, and 16 standalone recon tools. See everything in the platform.
Find reachable PLC, SCADA and fieldbus services such as Modbus, S7comm, EtherNet/IP and PROFINET before an attacker does.
Surface exposed device services (RTSP cameras, JetDirect printers, MQTT brokers, UPnP responders) across networks you are responsible for.
Audit internal infrastructure for legacy protocols, weak TLS and unauthenticated databases, with a tamper-evident audit trail.
Per-user, per-tool permissions, shareable target groups and scheduled scans for running assessments across multiple environments.
These are example use cases for the platform’s capabilities, not customer endorsements.
Memory-hard password hashing
Authenticator-app second factor
Hardware and platform authenticators
Invite-only Entra ID sign-in
Per-user, per-tool access levels
Hash-chained and tamper-evident
ThreatLark is self-hosted: scan data, credentials and reports stay inside your environment.
A distro-aware installer for Kali/Debian and RHEL families. It installs prerequisites, generates secrets and TLS, builds, and starts the service.
docker compose up -d --build builds an image with every scanner binary baked in. State lives in a single named volume.
A Manifest V3 companion that runs tech-detect, SSL/TLS, port, WHOIS and CVE lookups on the current tab through your signed-in session.
Book a walkthrough and see discovery, exposure scanning and prioritized findings running on your own network ranges.